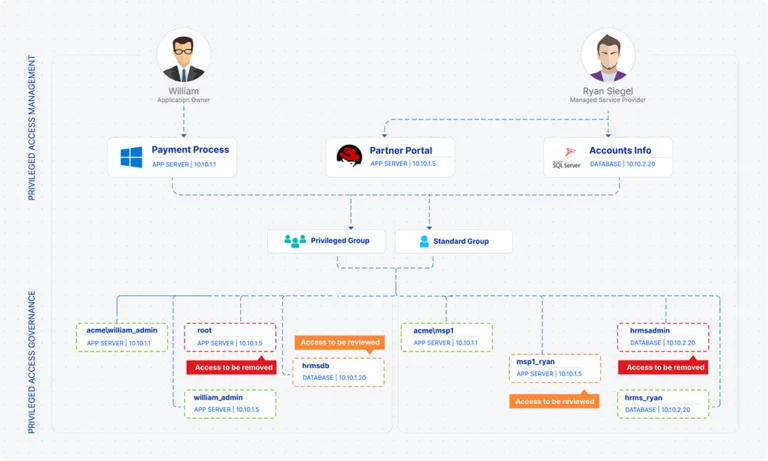
Effectively identify and manage potential risks associated with privileged user access, such as insider threats and accidental data breaches.
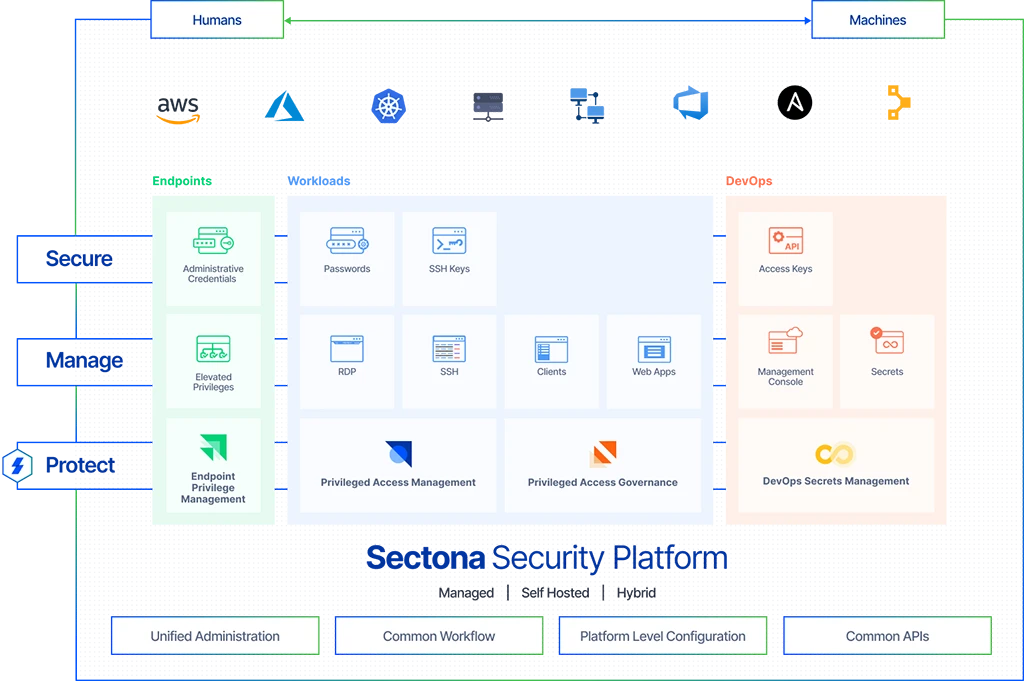
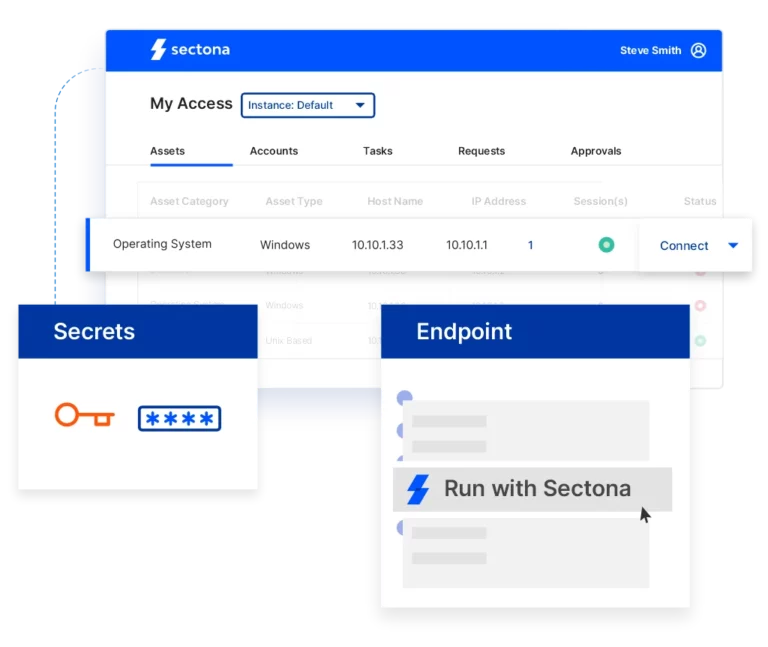
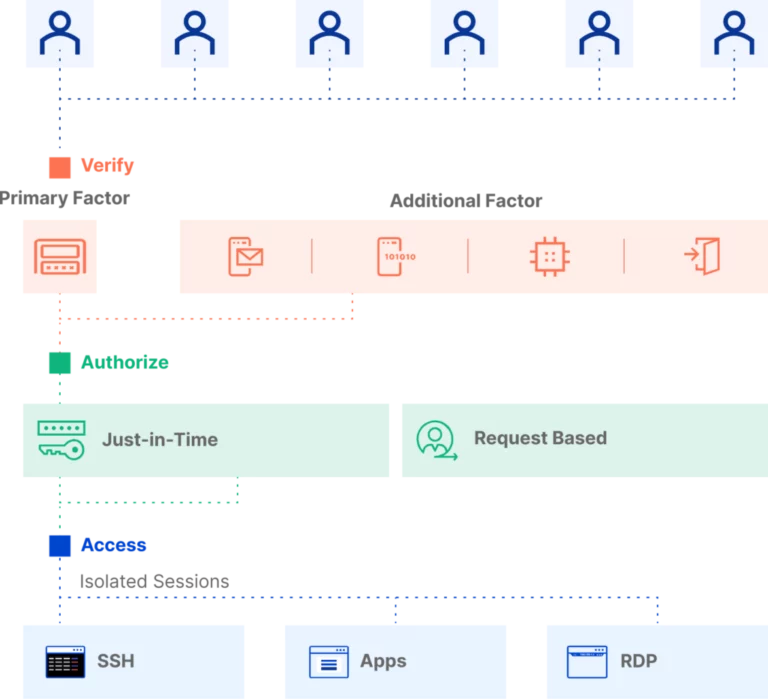
Secure passwords, SSH keys, and secrets within the solution’s purpose-built vault and isolate endpoints across each privileged session leveraging cross-platform session management technology.
Effectively identify and manage potential risks associated with privileged user access, such as insider threats and accidental data breaches.
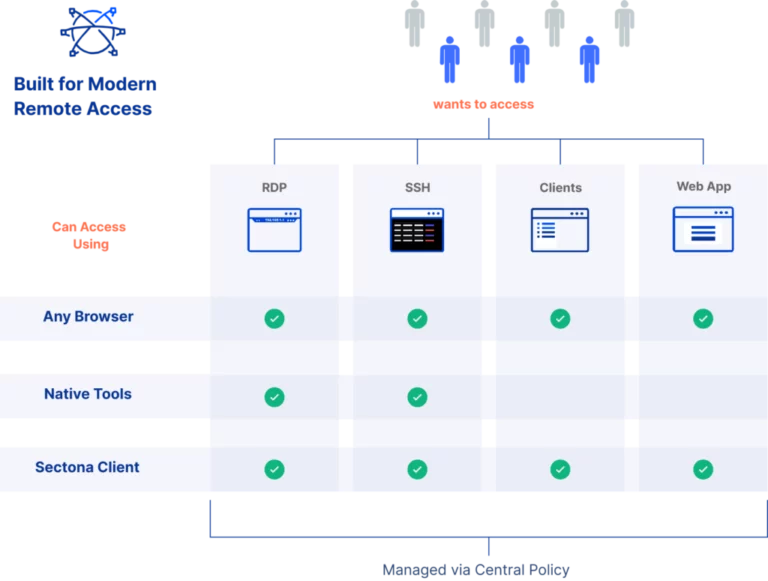
Leverage cross-platform session management technology to manage and govern privileged user access from anywhere
Define and streamline secure user access via browser, client, native utilities, or jump server, based on critical parameters
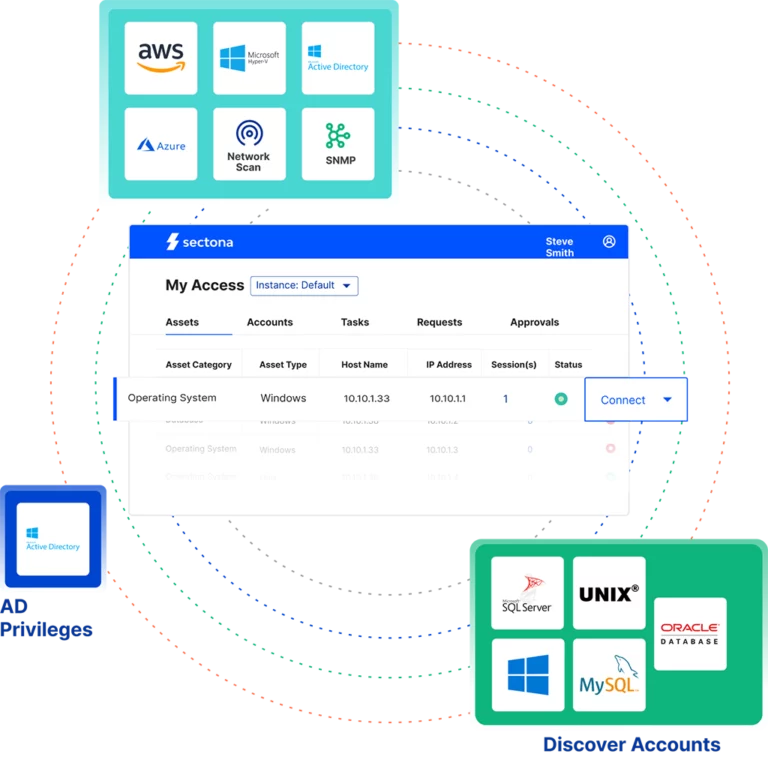
Simplify PAM operations and lifecycle with comprehensive discovery and onboarding at both asset and account level.
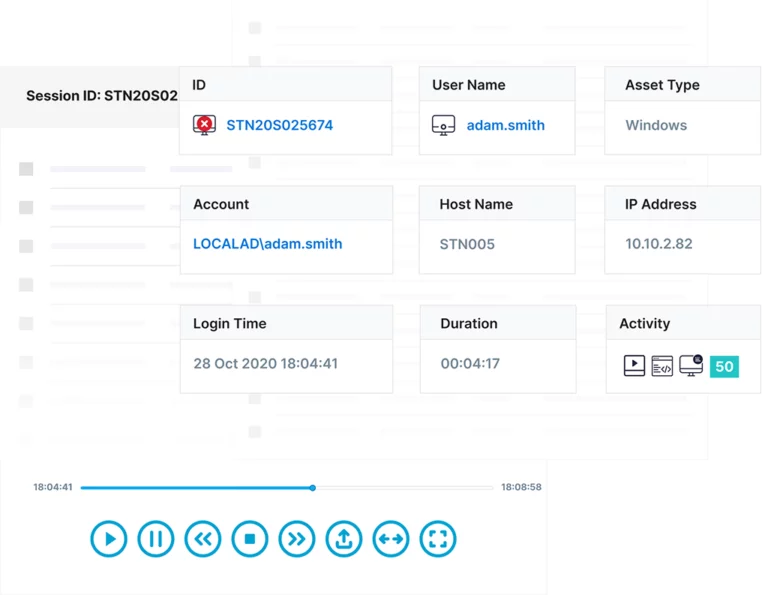
Track and maintain comprehensive logs of each privileged session while gathering risk-based threat intel.
Automate periodical review of entitlements and certification of access to PAM platform
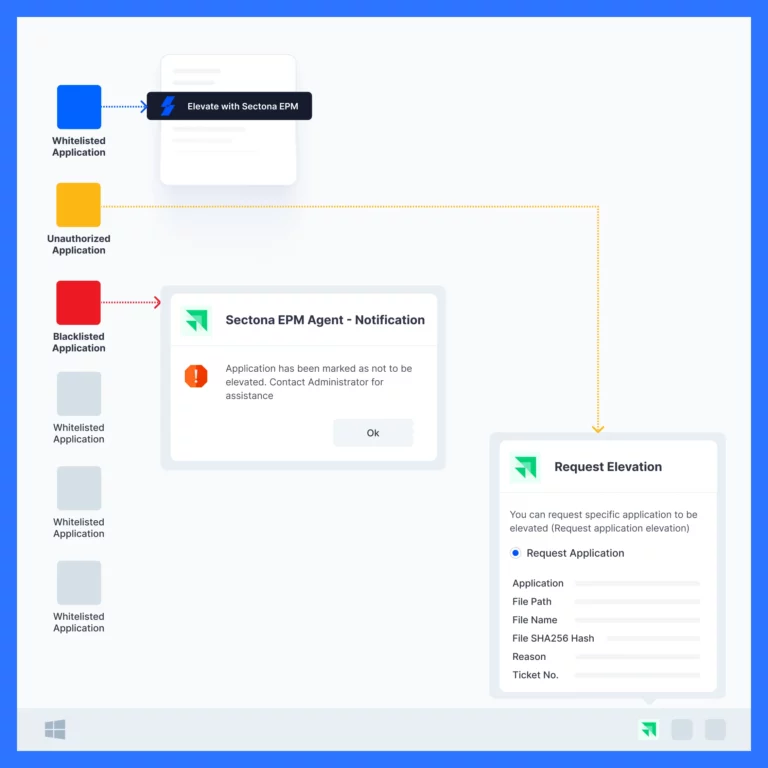
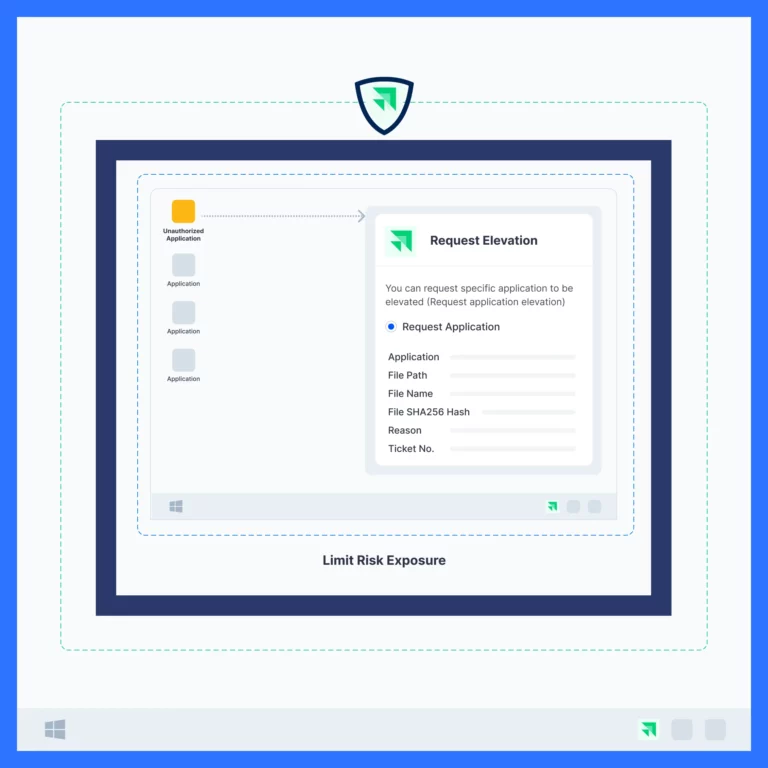
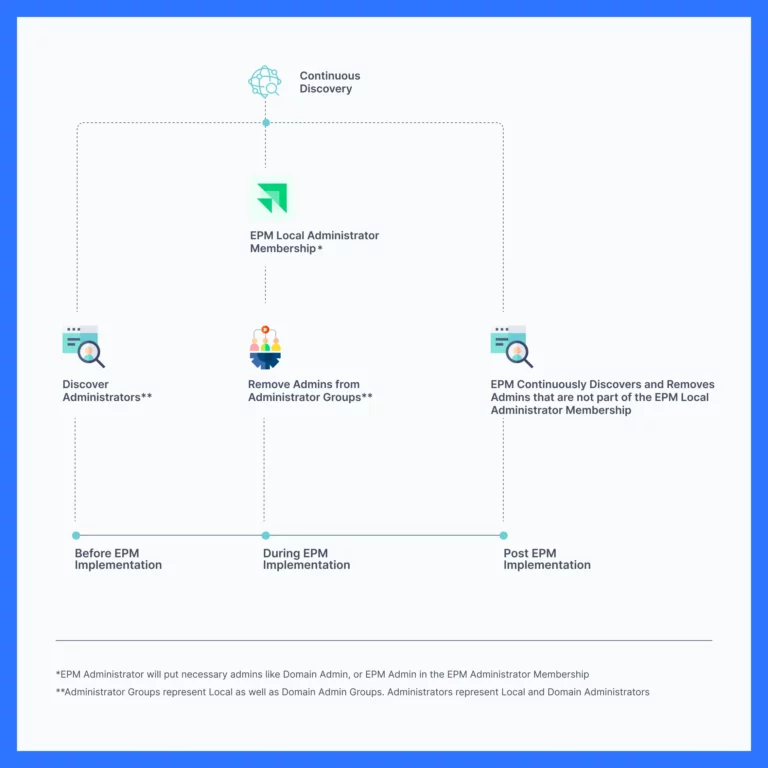
Endpoint Privilege Management works on securing administrator account usage on Windows systems that help control users’ privilege elevation and application access for improved & flexible IT.
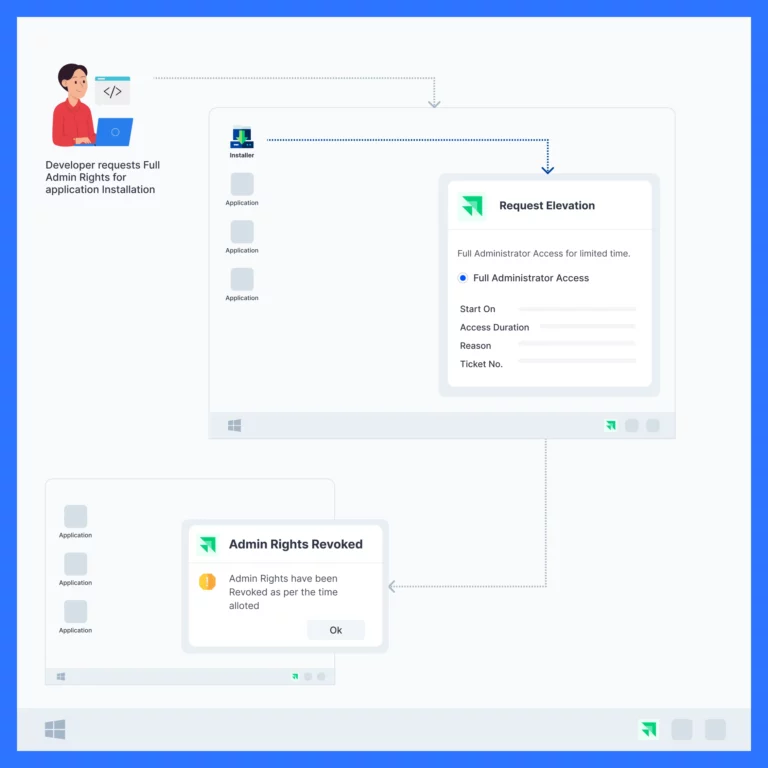
Users can request administrator rights and access for a specific application or for a defined time to perform administrative activities.
Enable users to access trusted applications only and facilitate request-based access otherwise.
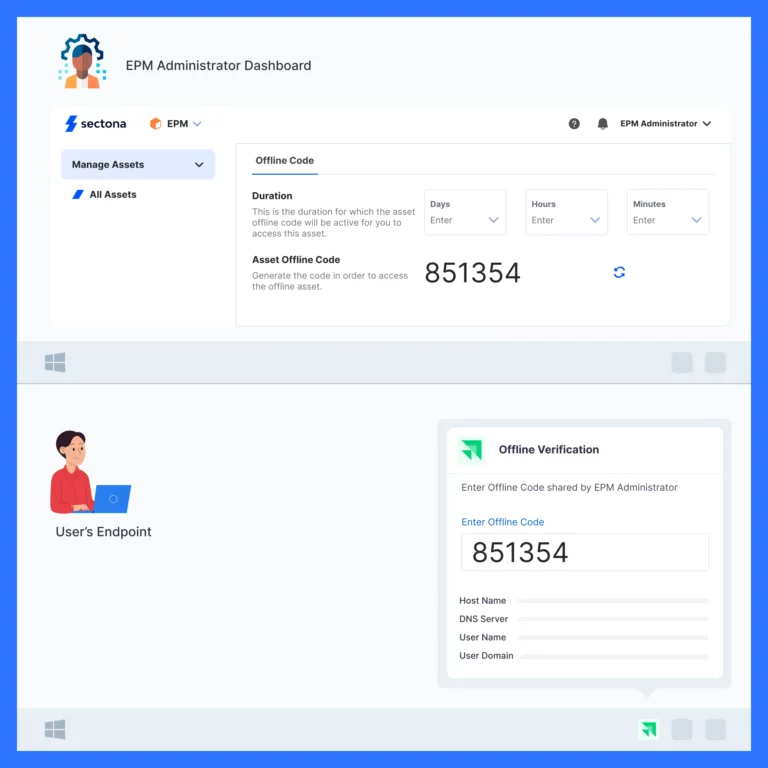
Authorize remote workforce outside LAN or without internet to access securely.
Stay in control of administrator rights granted over a period of time and keep track of usage of local administrator privileges with special reports.